 WIUNIX ACADEMY
Find which Linux process is listening on a port
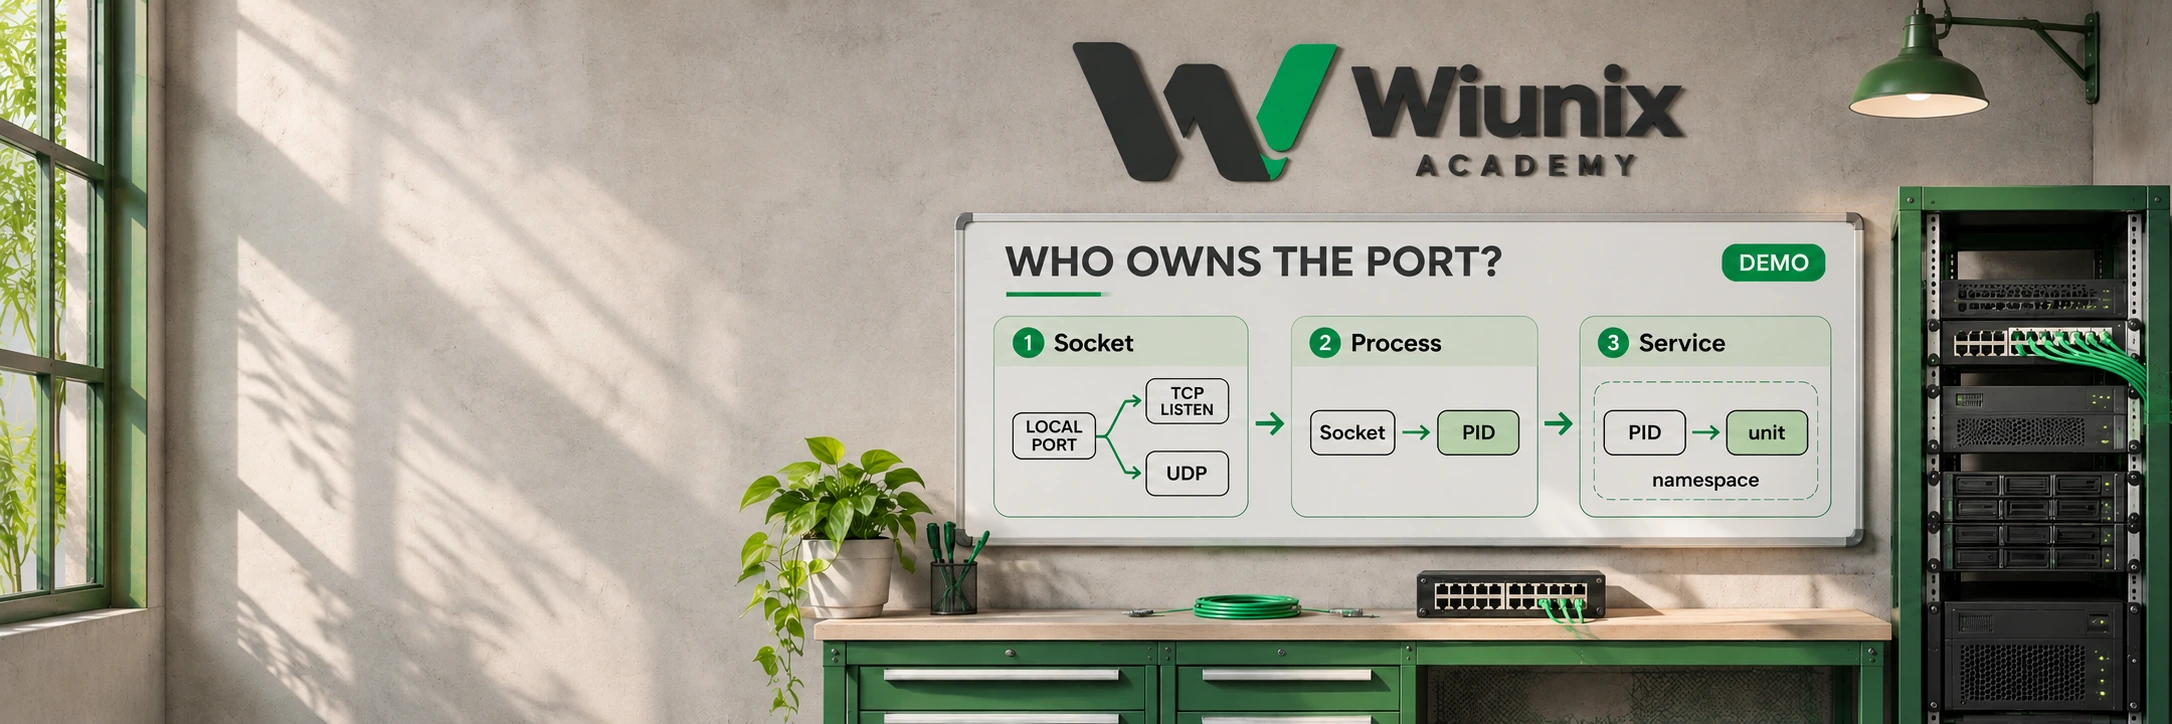
A service won't start because the address is already in use? Trace a local TCP or UDP port to its socket, process and service before deciding what to change.
Make this guide yoursYOUR SYSTEM. YOUR STEPS.
Where are you working?
Choose your OS and version. The prerequisites, commands and troubleshooting follow your environment.
THE OUTCOME
What will you have at the end?
A service won't start because the address is already in use? Trace a local TCP or UDP port to its socket, process and service before deciding what to change.
Supported operating systems and versions
Documentation-reviewed paths for Ubuntu, Debian, RHEL, Rocky Linux, AlmaLinux, Arch Linux and Manjaro. The workflow reads Linux socket tables; the commands do not apply on Windows or macOS.
Before you begin
- Access to the affected Linux host, the port and protocol from the error, and sudo permission only if you need to see another account's PID.
- Use the example port 8080 or replace it with the actual local port in both socket checks.
Start with the bind error
Keep the protocol, address and port from the error. A TCP listener and a UDP socket can use the same number. Two TCP sockets can also coexist on different local addresses; a wildcard bind can cover more than the address you were checking.
The socket table is local to a network namespace. Start on the machine where the bind failed. A successful lookup doesn't establish that a client can reach that address through a firewall or a container port mapping.
LET’S BUILD
Check that ss is available
Run this on the affected host to confirm the distribution and locate ss. If it is missing, ask the host owner to prepare the package from the distribution’s own repository.
The package is iproute2 on Ubuntu, Debian and the Arch family, and iproute on RHEL, Rocky and AlmaLinux. The command below only queries the installed package.
Authorized terminal on the affected host
cat /etc/os-release
dpkg-query -W iproute2
command -v ss
ss -VThe release and installed ss version are visible; if ss is absent, stop before the socket lookup.
LET’S BUILD
Look up TCP listeners on the exact local port
Use the source-port filter because you are looking for the local endpoint. Numeric output preserves exact addresses and ports. Look at Local Address:Port and the process field. A loopback listener is local; an IPv4 wildcard covers local IPv4 interfaces, while an IPv6 wildcard may also accept IPv4 depending on the socket setting.
If the table shows a socket without a process name, repeat the check with sudo only when authorized. Empty output means no matching TCP listener was visible in this namespace at that instant; a quickly restarting service can change the result.
Authorized terminal on the affected host
ss -ltnp 'sport = :8080'Matching LISTEN rows show their local bind address and, when visible, process name and PID.
LET’S BUILD
Check UDP separately
UDP has no TCP listen handshake. Ask for all UDP sockets whose local port matches. UNCONN is normal for a socket with no fixed peer; an associated peer is also possible. Do not treat either state as proof that requests are being answered.
Authorized terminal on the affected host
ss -uanp 'sport = :8080'Any matching UDP rows are visible independently of the TCP result.
LET’S BUILD
Match the PID to a service or socket unit
Replace the example PID with the current value from ss. Inspect basic identity rather than dumping command arguments that might contain a secret. On a systemd host, status can map a PID to its unit. When the listener belongs to PID 1 or appears to be socket-activated, inspect the socket list and compare its Listen address and Activates column.
Use the owner’s service or container configuration for any eventual change. The same PID can be reused after exit, and multiple workers may share an inherited socket. Re-run the port filter before acting if the service is unstable.
Authorized terminal on the affected host
pid=1234
ps -p "$pid" -o pid,ppid,user,comm
systemctl status "$pid" --no-pager -n 0
systemctl list-sockets --all --no-pagerThe PID is tied to a unit, a socket activation entry or an unmanaged process. A failed unit lookup doesn't mean the process is absent.
If the host table disagrees with the application
If a container gets the bind error, repeat the lookup inside its network namespace using the approved runtime access. The host table alone cannot rule out a conflict there. Conversely, a runtime can publish a host port with packet translation and no corresponding host process in ss.
This workflow is read-only; there is nothing to undo. If you later change a bind address or port, keep the previous configuration, coordinate dependent proxies, and verify both the new local socket and an authorized client request. Restore the old configuration with the native service procedure if the change fails.
The socket appears but the process is hidden
With approval, inspect the same port with process visibility. A disappearing row can simply mean the process exited.
sudo ss -ltnp 'sport = :8080'
sudo ss -uanp 'sport = :8080'
GO TO THE SOURCE
Official references
Each environment states how it was reviewed. A documentation review does not claim a hands-on test of every version.
KEEP LEARNING