
WIUNIX ACADEMY
Practical knowledge. Better systems.
Tutorials for building, securing and operating your infrastructure. Find a topic, follow the steps and put what you learn to work.
WIUNIX ACADEMY
Tutorials for building, securing and operating your infrastructure. Find a topic, follow the steps and put what you learn to work.
START WITH A QUESTION
FIND YOUR FOCUS
From infrastructure fundamentals to the everyday work of IT teams.
Linux, service management and availability.
Routing, VPNs and connecting your systems.
Protect services and manage trusted access.
Web servers, HTTPS, caching and databases.
Application containers and virtual environments.
Storage, recovery, metrics and service health.
TAKE A CLOSER LOOK
Databases
Build a fresh PostgreSQL18/Patroni lab with TLS, three-member etcd quorum, WAL checks and a planned switchover, with explicit fencing and recovery limits.
Read tutorialSecurity
Trace repeated HTTP authentication failures from a minimal Nginx log to a dedicated jail, rehearse safely, then activate a narrowly scoped host firewall action.
Read tutorialMonitoring
Build a private monitoring stack with pinned images, service discovery, provisioned dashboards, persistent data and a safe backup/restore rehearsal.
Read tutorialTHE KNOWLEDGE LIBRARY
20 tutorials · Page 1 / 2
Choose a resilient topology, separate API and console exposure, create scoped policies, enable versioning, and test restore paths.
Read tutorialParse trustworthy logs, evaluate scenarios, enforce decisions at Nginx, and test remediation without creating a new outage path.
Read tutorialDeploy Vaultwarden on loopback, protect the admin token, proxy it safely, and prove recovery before storing real credentials.
Read tutorialDeploy CNCF Distribution with persistent storage, bcrypt authentication, correct proxy headers, backups, and push/pull verification.
Read tutorialCombine certificate identity, PAM-backed TOTP, recovery controls, and staged rollout without weakening the VPN's TLS layer.
Read tutorialBuild a certificate bundle, preserve ACME renewal, validate proxy headers, and roll backend changes safely.
Read tutorialReplace static route sprawl with filtered BGP sessions over encrypted point-to-point tunnels.
Read tutorial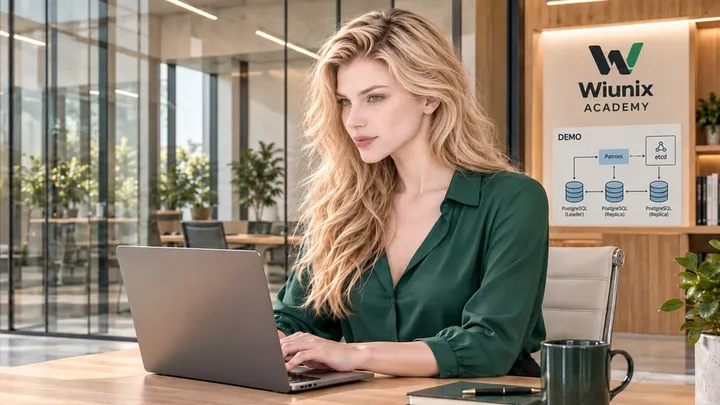
Build a fresh PostgreSQL18/Patroni lab with TLS, three-member etcd quorum, WAL checks and a planned switchover, with explicit fencing and recovery limits.
Read tutorial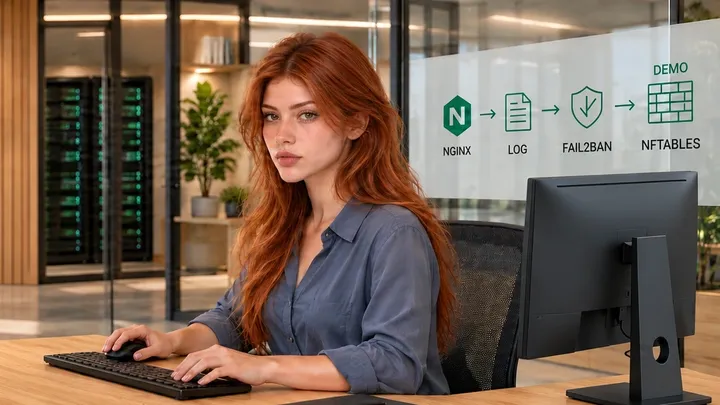
Trace repeated HTTP authentication failures from a minimal Nginx log to a dedicated jail, rehearse safely, then activate a narrowly scoped host firewall action.
Read tutorial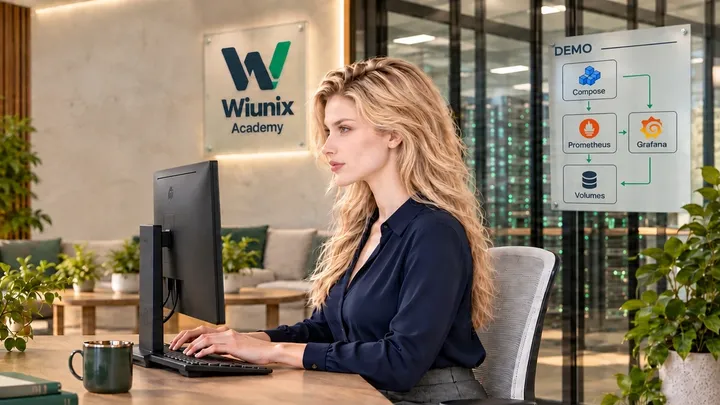
Build a private monitoring stack with pinned images, service discovery, provisioned dashboards, persistent data and a safe backup/restore rehearsal.
Read tutorial
Build a dedicated Traefik edge with verified TLS, a loopback origin and private dashboard. Separate staging from production, prove HTTP/3 and protect certificate recovery.
Read tutorial
Choose your Linux version, install Caddy, connect a private backend and verify automatic HTTPS—with copyable commands, expected results and fixes for common errors.
Read tutorial